SOC 2 Compliance Software
for Small Teams

A US customer wants your SOC 2 report before they sign. ComplyDog walks you through what the auditor will look at, in plain English, so your team understands every control before the audit starts.

No credit card required
Trusted by Software Companies

Logo Logo Logo Logo FlybyOps Logo Logo Logo Logo

How ComplyDog Gets You Ready for SOC 2

Plain English, Not Audit-Speak

Plain English, Not Audit-Speak

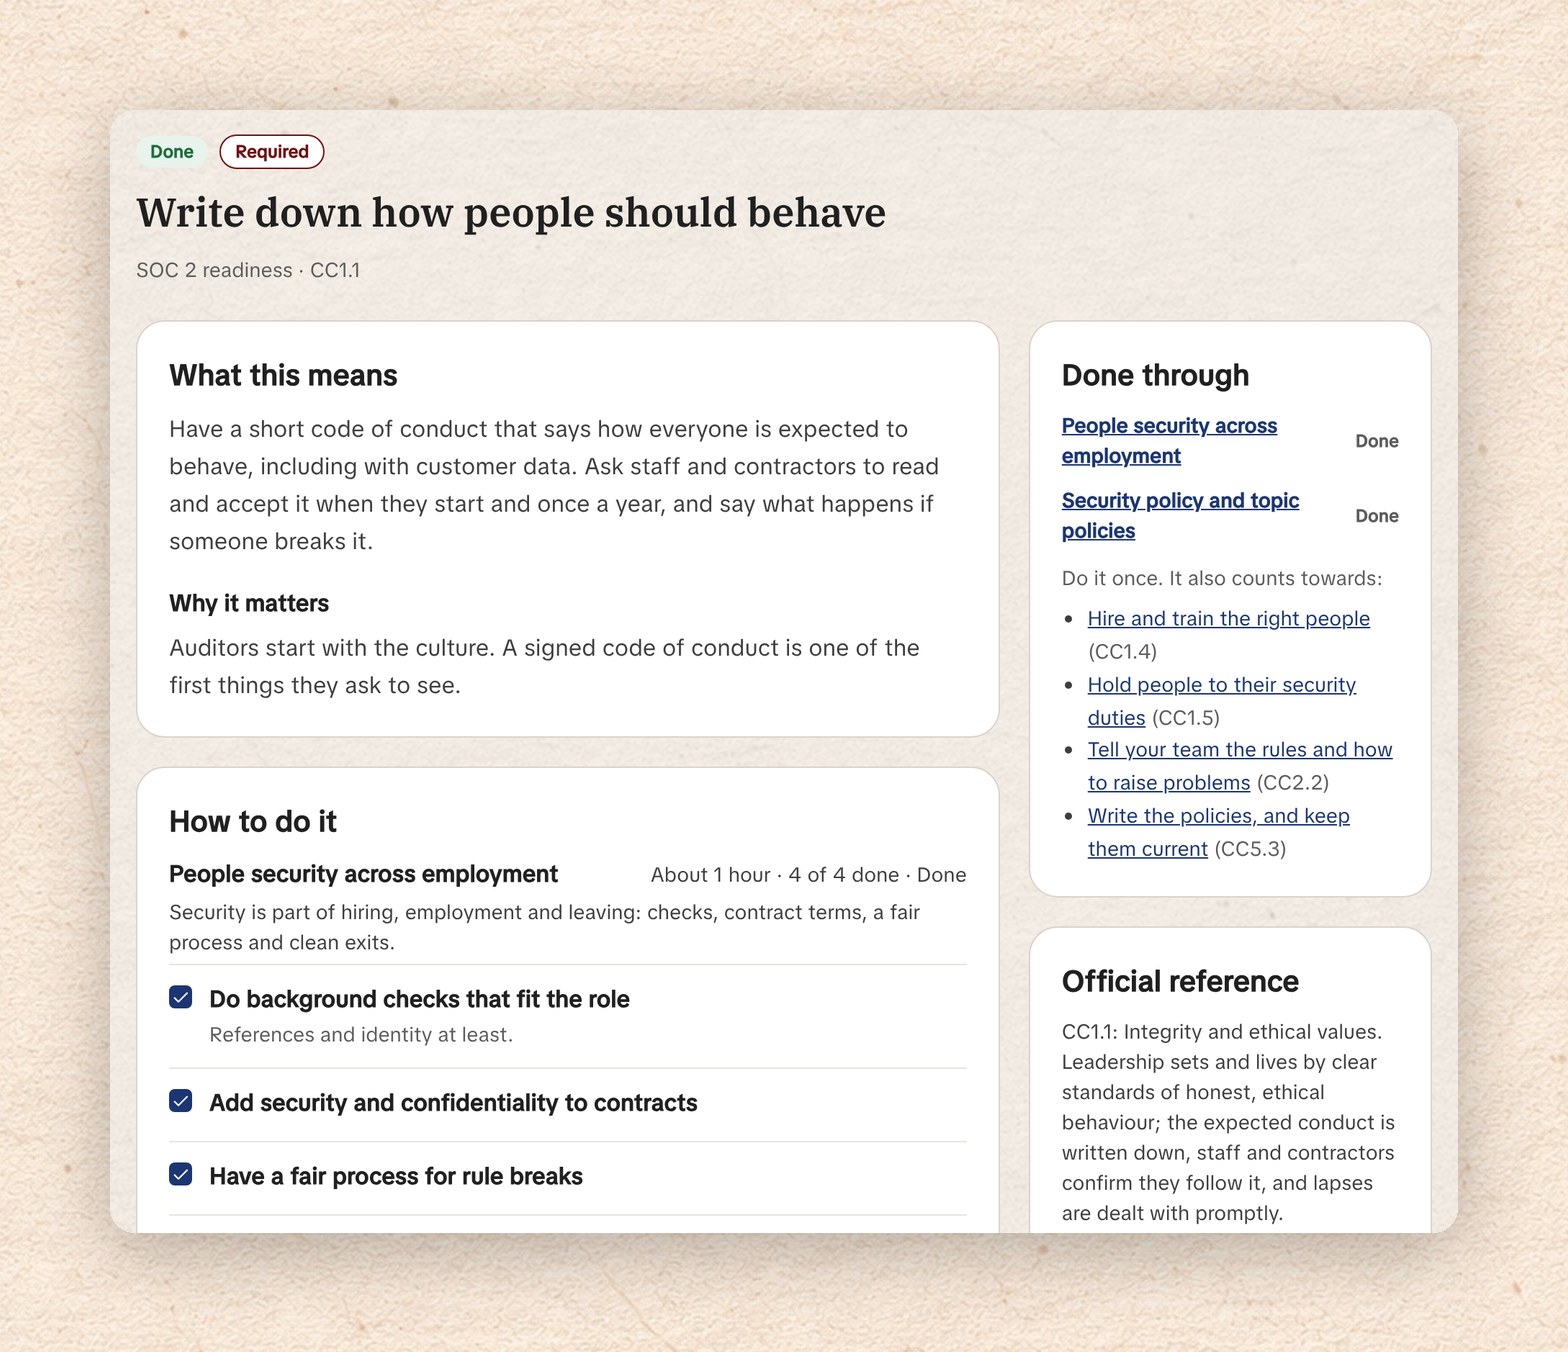
Every criterion explained: what the auditor looks for, why it matters, how to do it and what counts as proof.

Reuse Your ISO 27001 Work

Reuse Your ISO 27001 Work

SOC 2's security criteria cover much of the same ground as ISO 27001, and ComplyDog maps both to the same safeguards. Started one? You've started both.

Type I or Type II, Explained

Type I or Type II, Explained

Understand the difference before you pick an auditor, and plan the period your controls need to run for.

Features

Everything You Need Before Your SOC 2 Audit

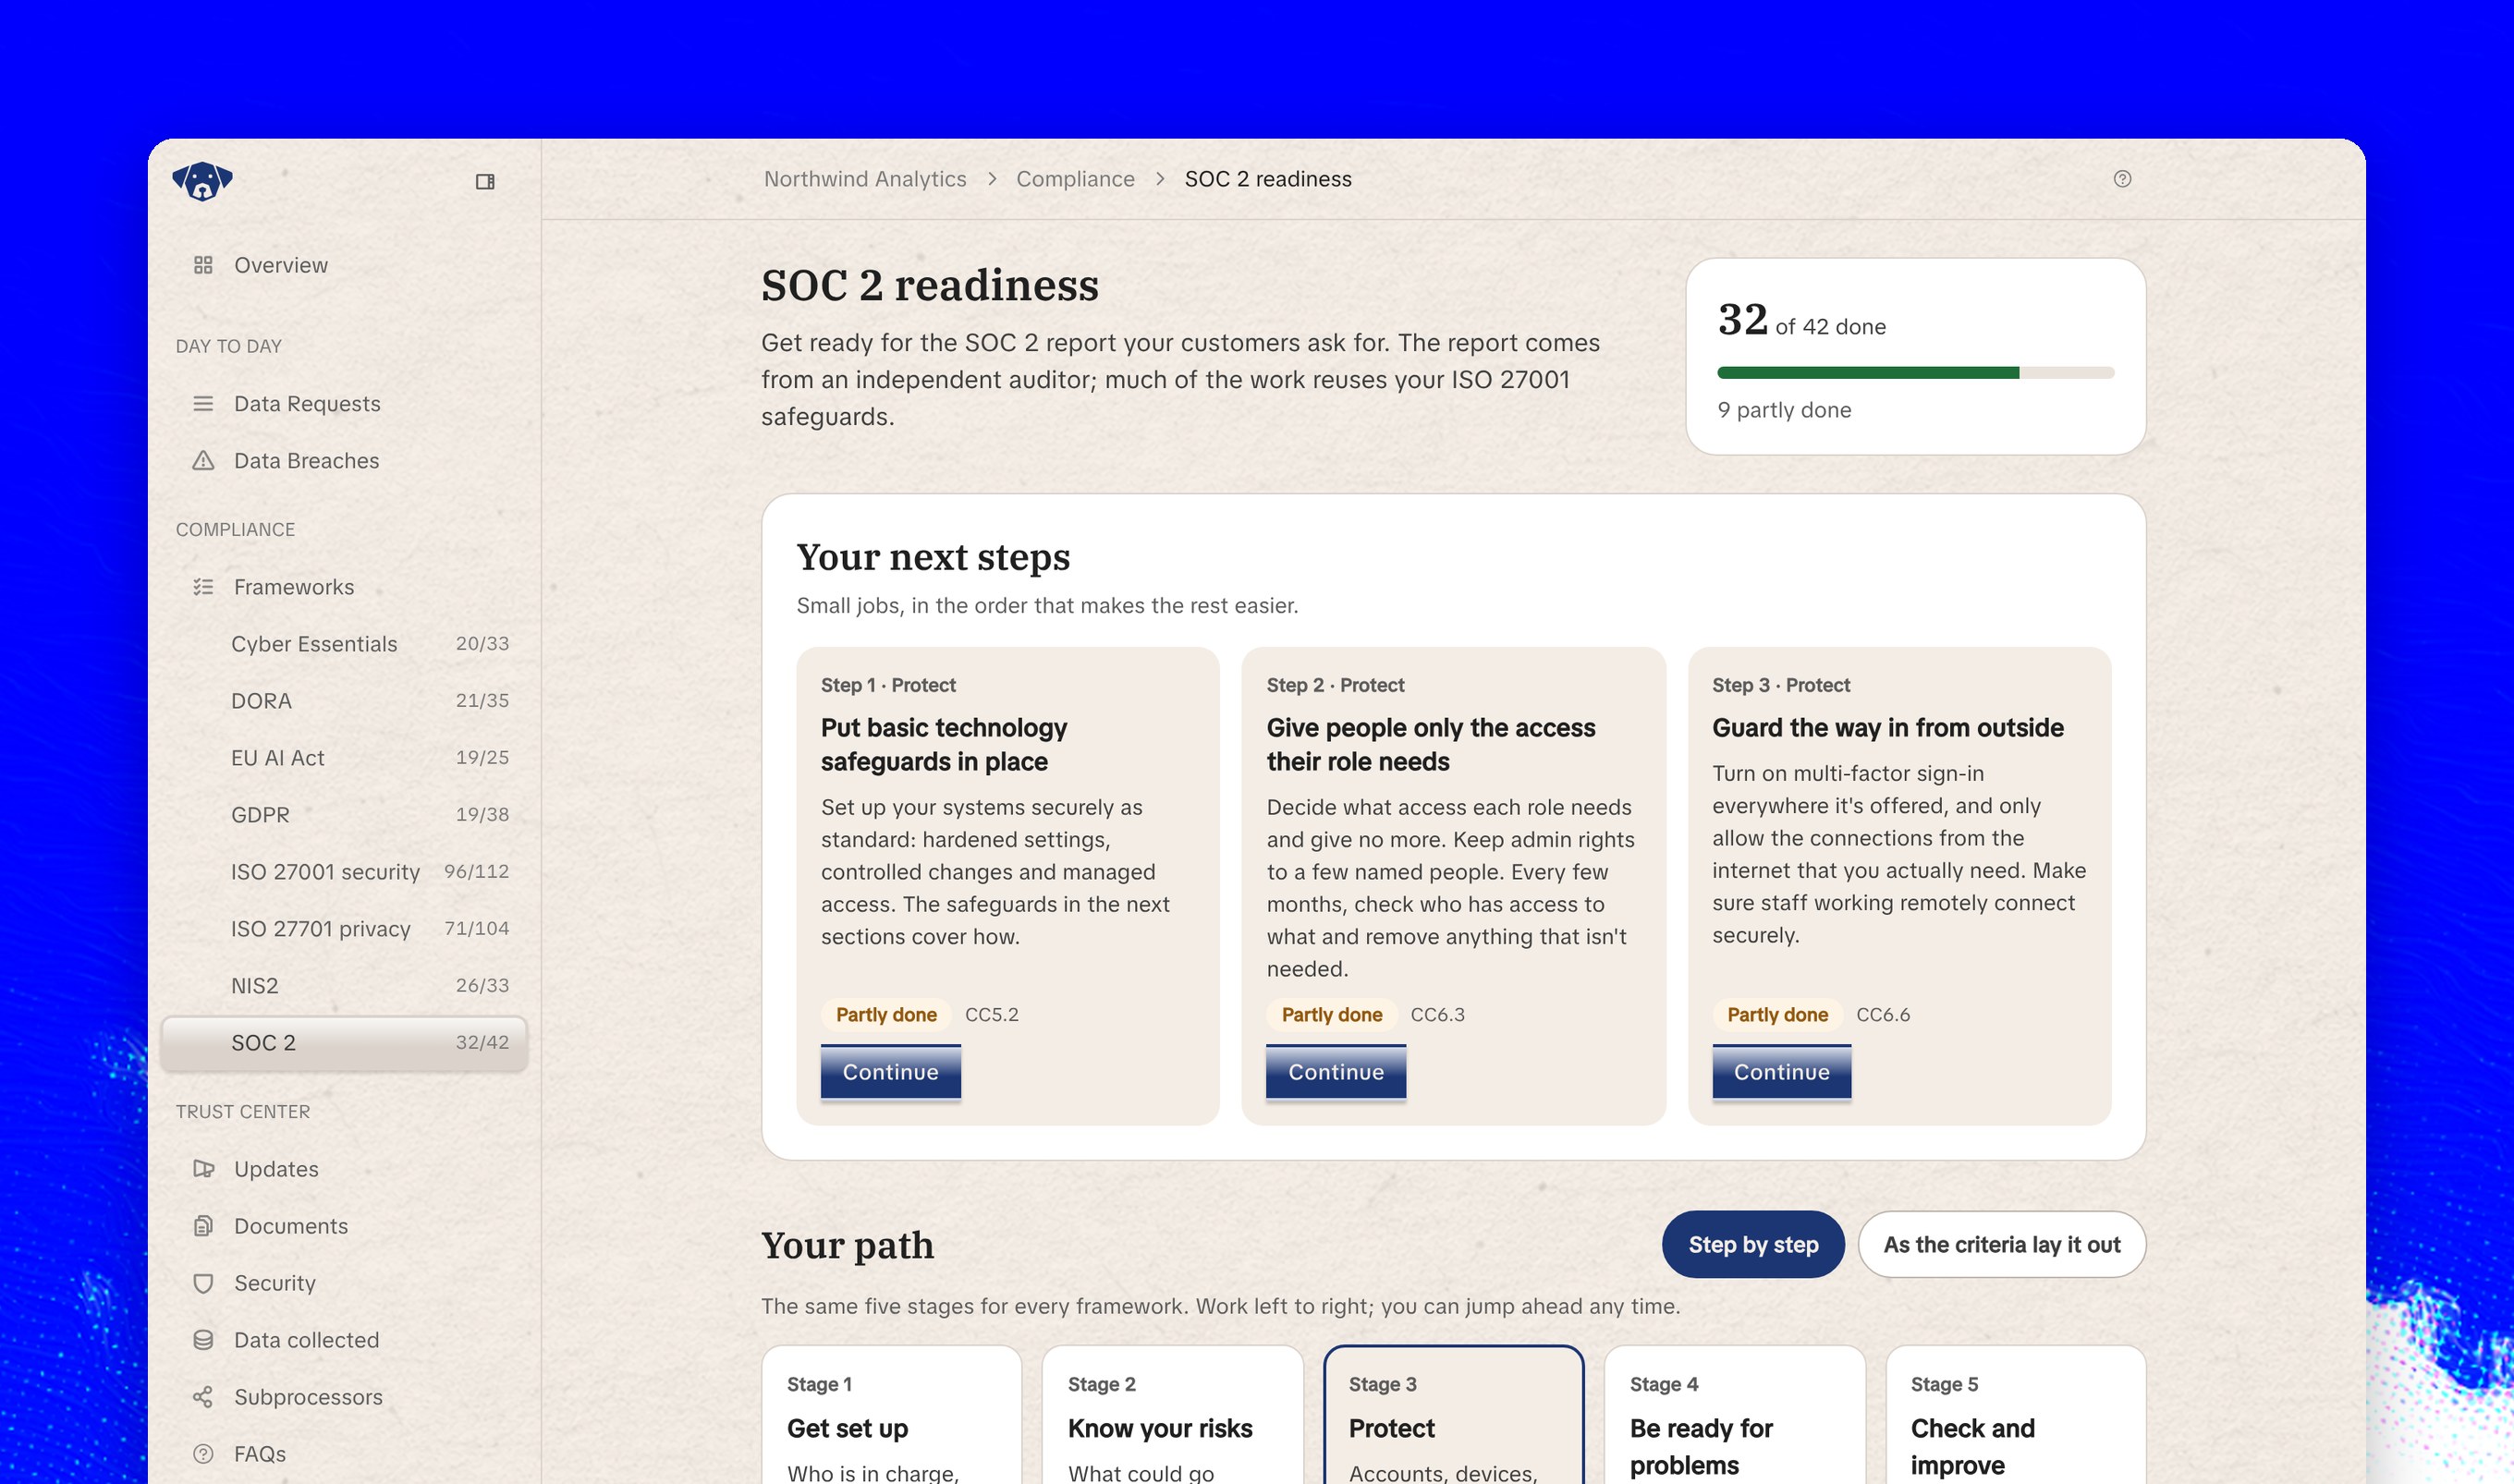
Readiness Score

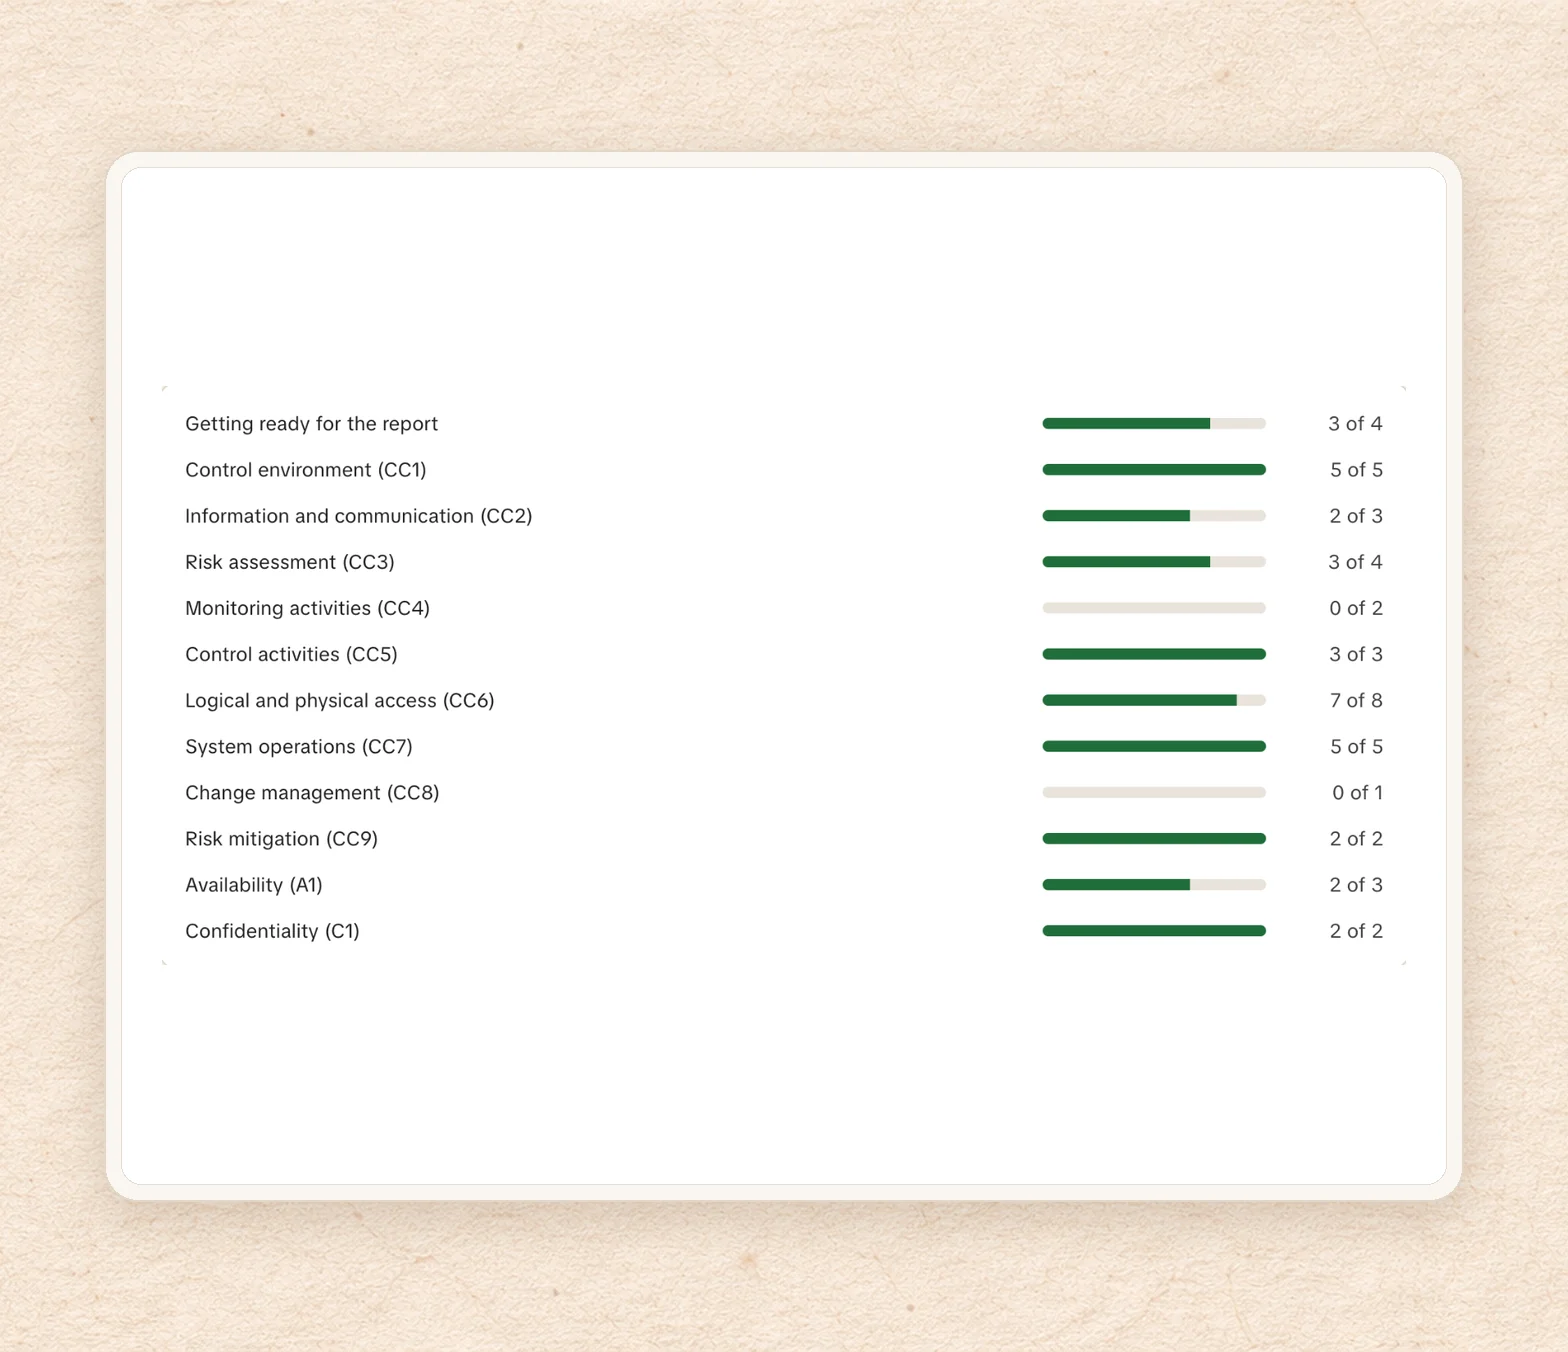
See how ready you are overall and for each criteria group.

Safeguards and Proof

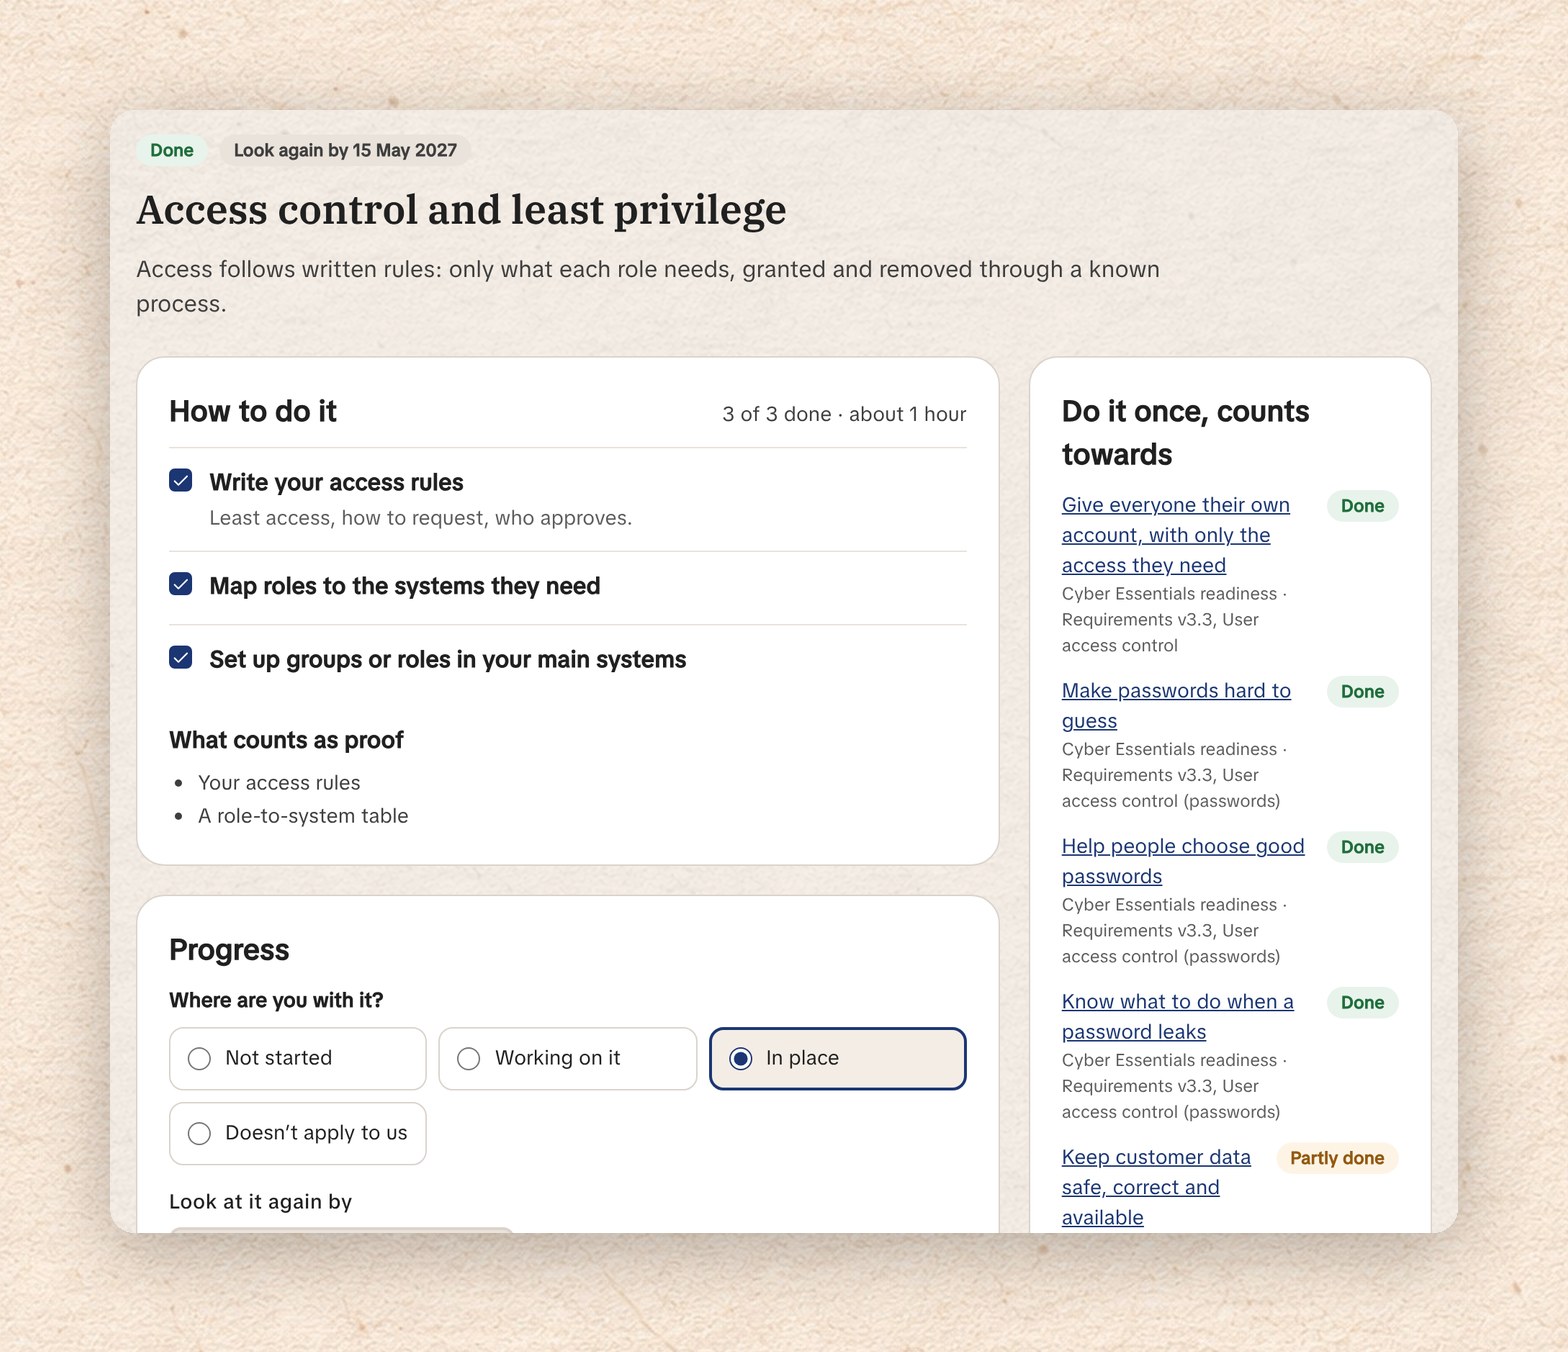
Mark each safeguard in place and add files, notes or links as proof. Reuse the same proof wherever it counts.

Policy Templates

Start from plain-English policies, then make them yours.

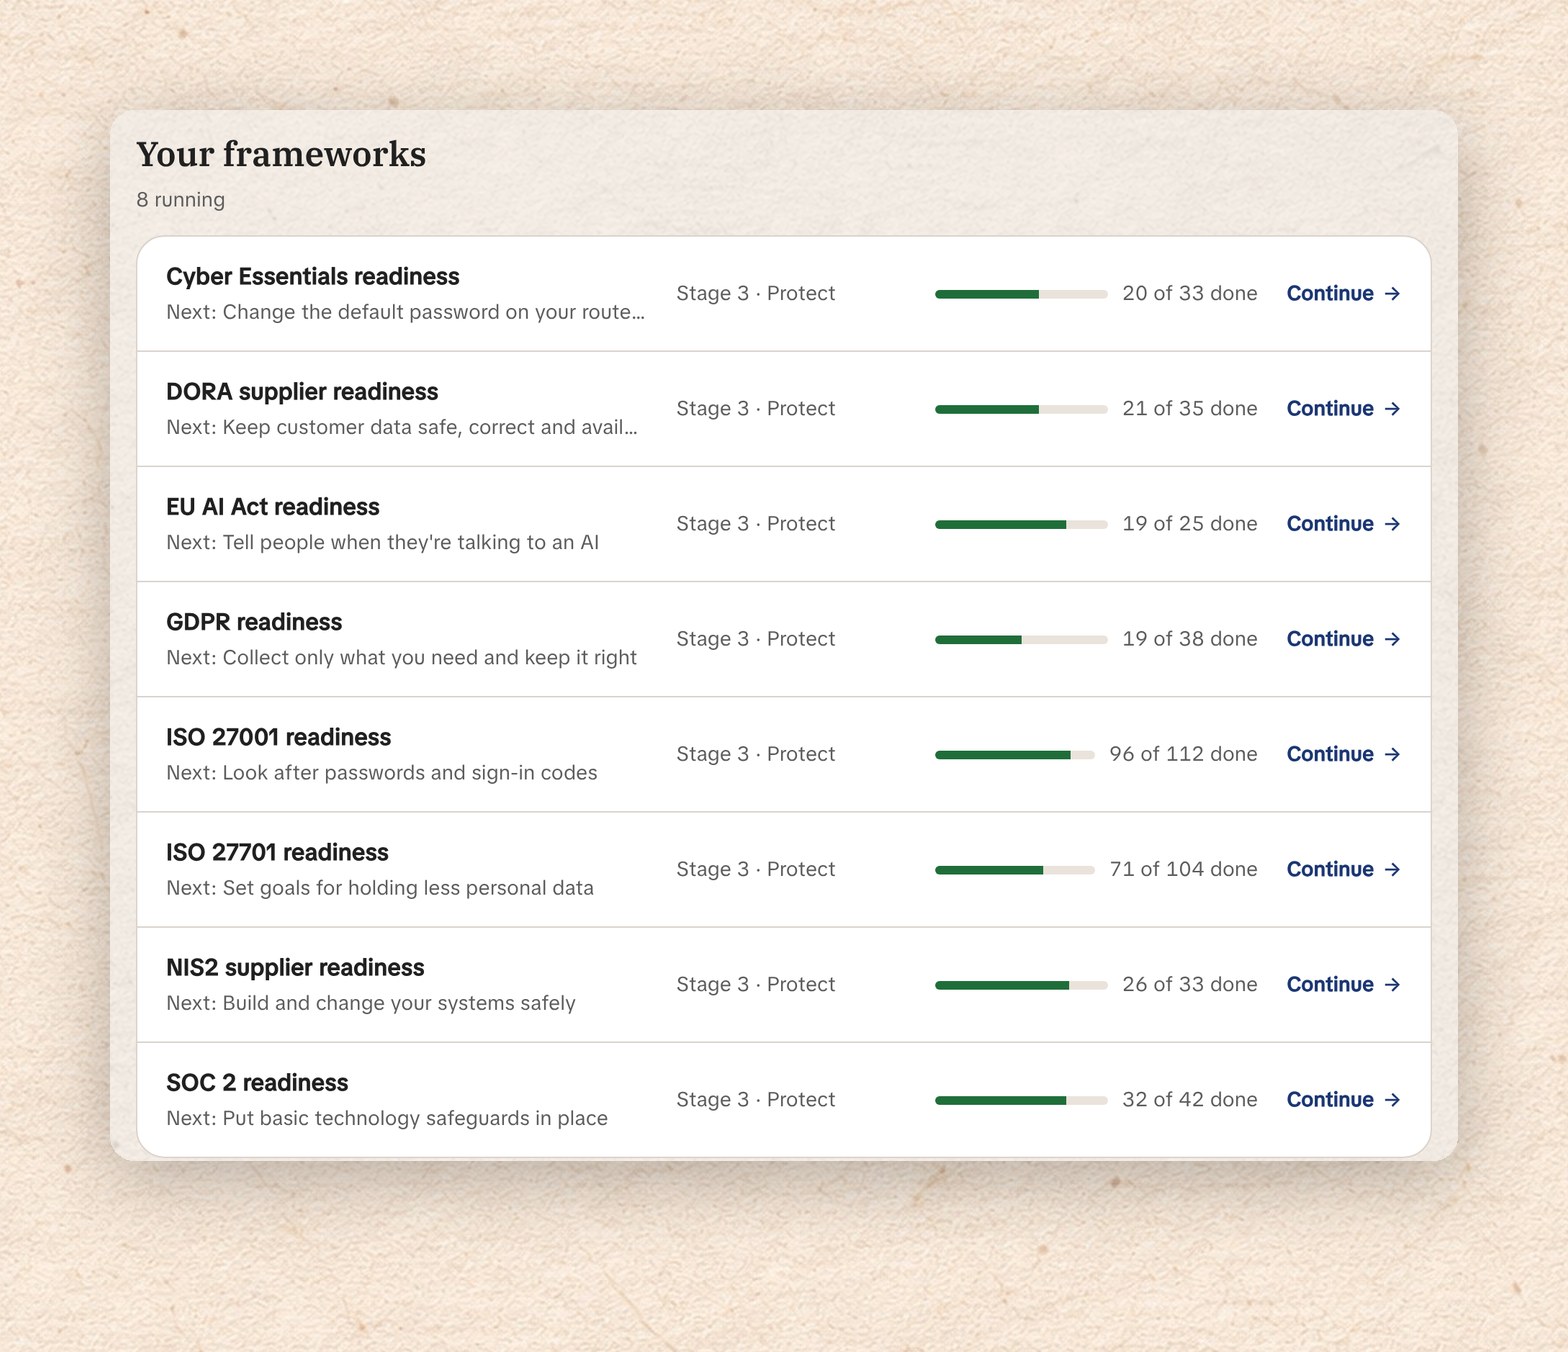
Shared With ISO 27001, NIS2 and GDPR

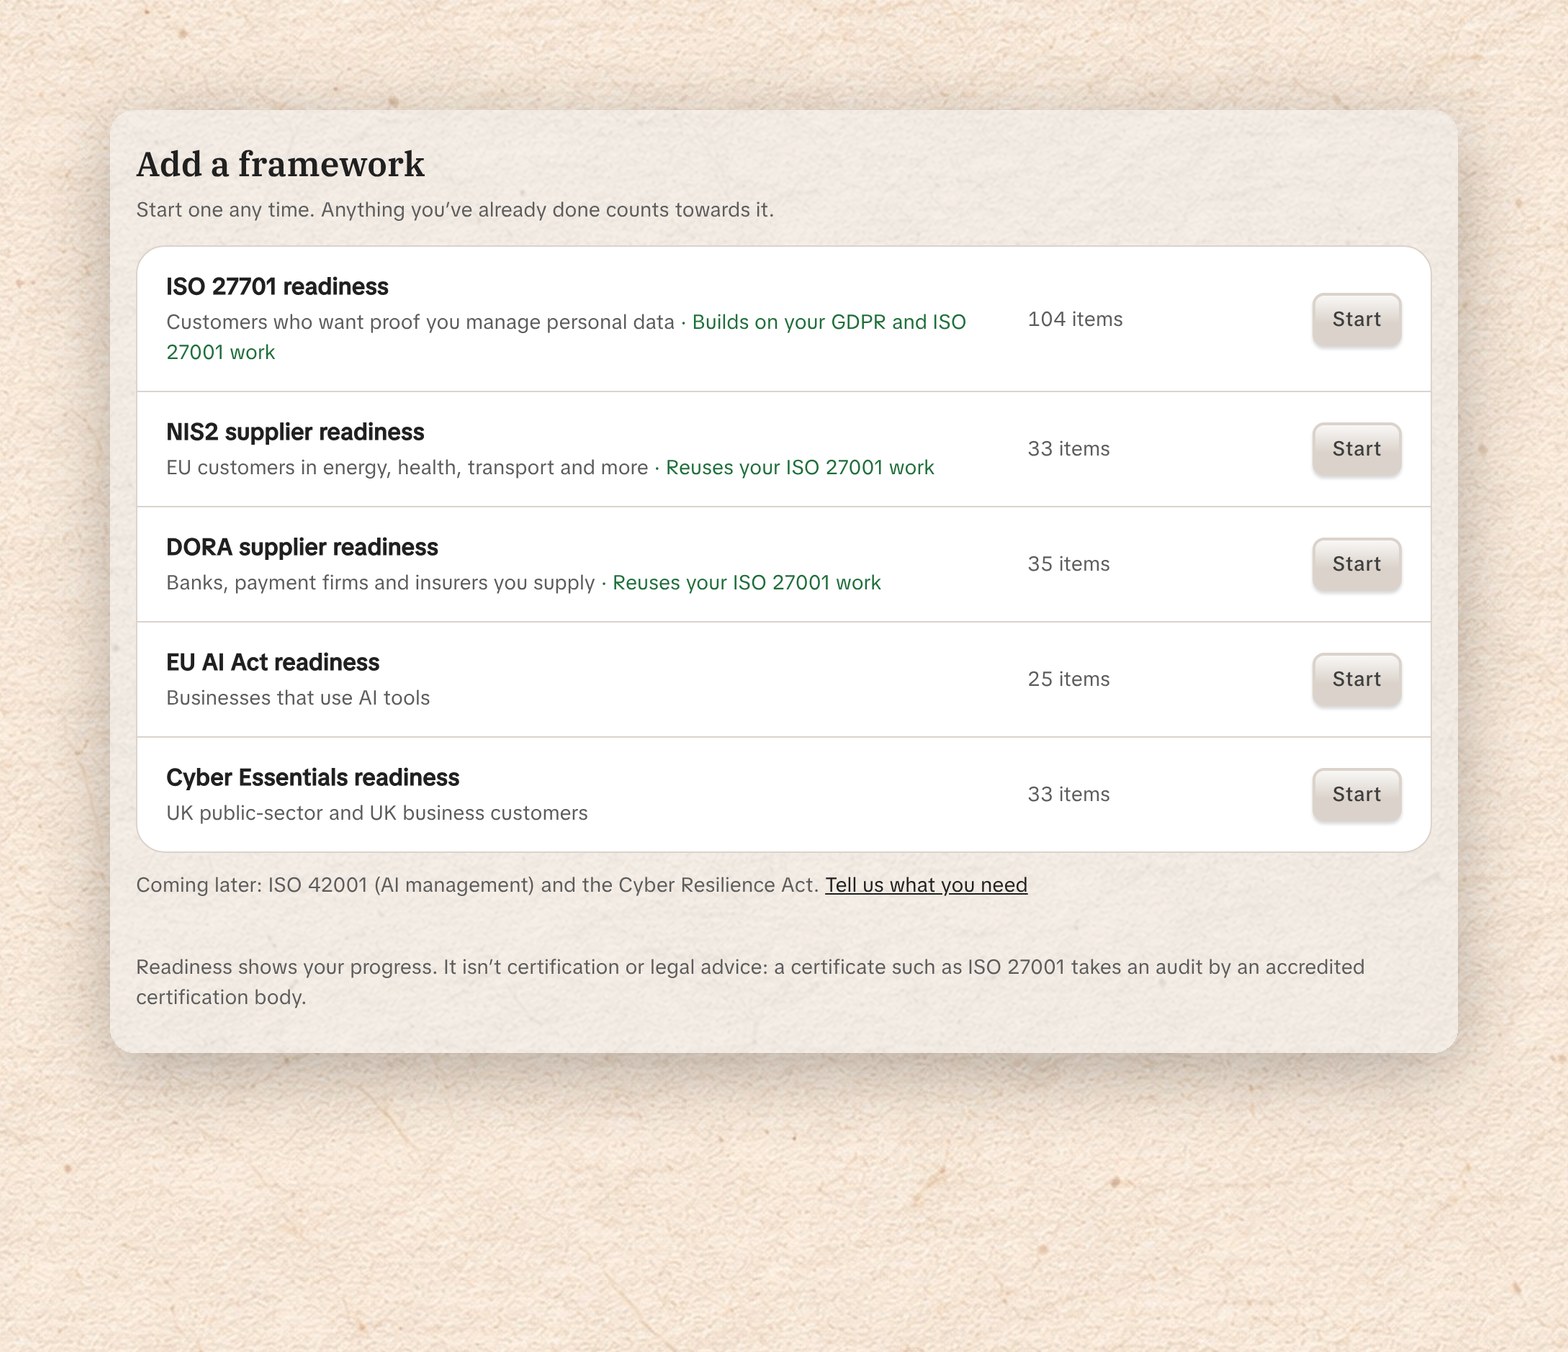
The work you do here counts towards your other frameworks.

Full History

See who changed what and when, so you can show the auditor how decisions were made.

Trust Center

Show customers you're working towards SOC 2, then that you're ready for the audit.

How It Works

SOC 2 Ready in 3 Steps

1. Add SOC 2

1. Add SOC 2

Security is always in scope. Choose any other categories your customers need.

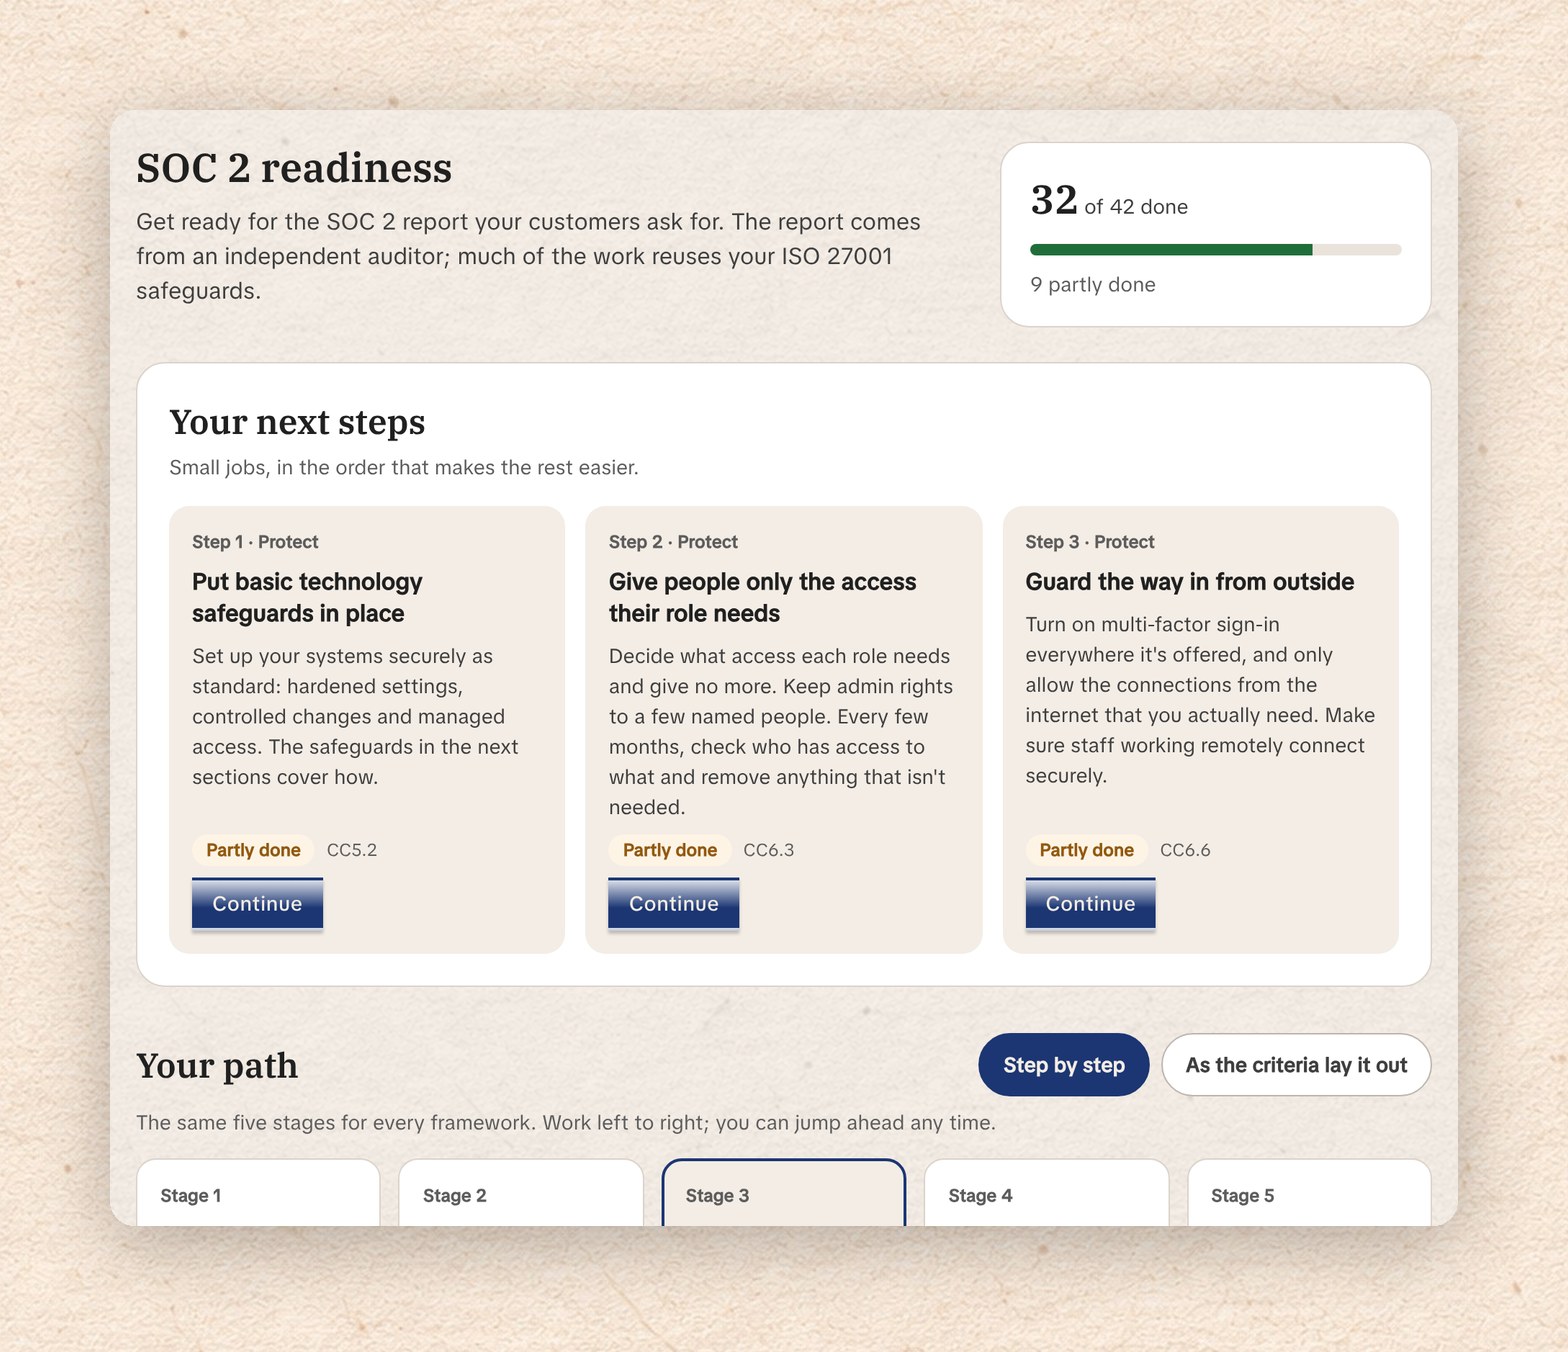
2. Work Through Your Next Steps

2. Work Through Your Next Steps

Tick off small tasks and add proof as you go.

3. Pick Your Auditor

3. Pick Your Auditor

When you're ready, a licensed CPA firm does the audit and writes your report. ComplyDog gets you ready for it.

No credit card required
Frequently Asked Questions

Not exactly. SOC 2 is an audit report from a CPA firm, not a certificate. Customers ask for the report.

Type I checks your controls are designed properly at one point in time. Type II checks they worked over a period, usually 3 to 12 months. Most buyers want Type II.

No. A licensed CPA firm does. ComplyDog gets your team ready and keeps your proof in one place.

It depends on your customers. US buyers usually ask for SOC 2, European buyers for ISO 27001. ComplyDog lets you work on both with the same safeguards.

Read more: SOC 2 vs GDPR · ISO 27001 readiness

Try It Free for 14 Days,
See if It's Right for You

No credit card required