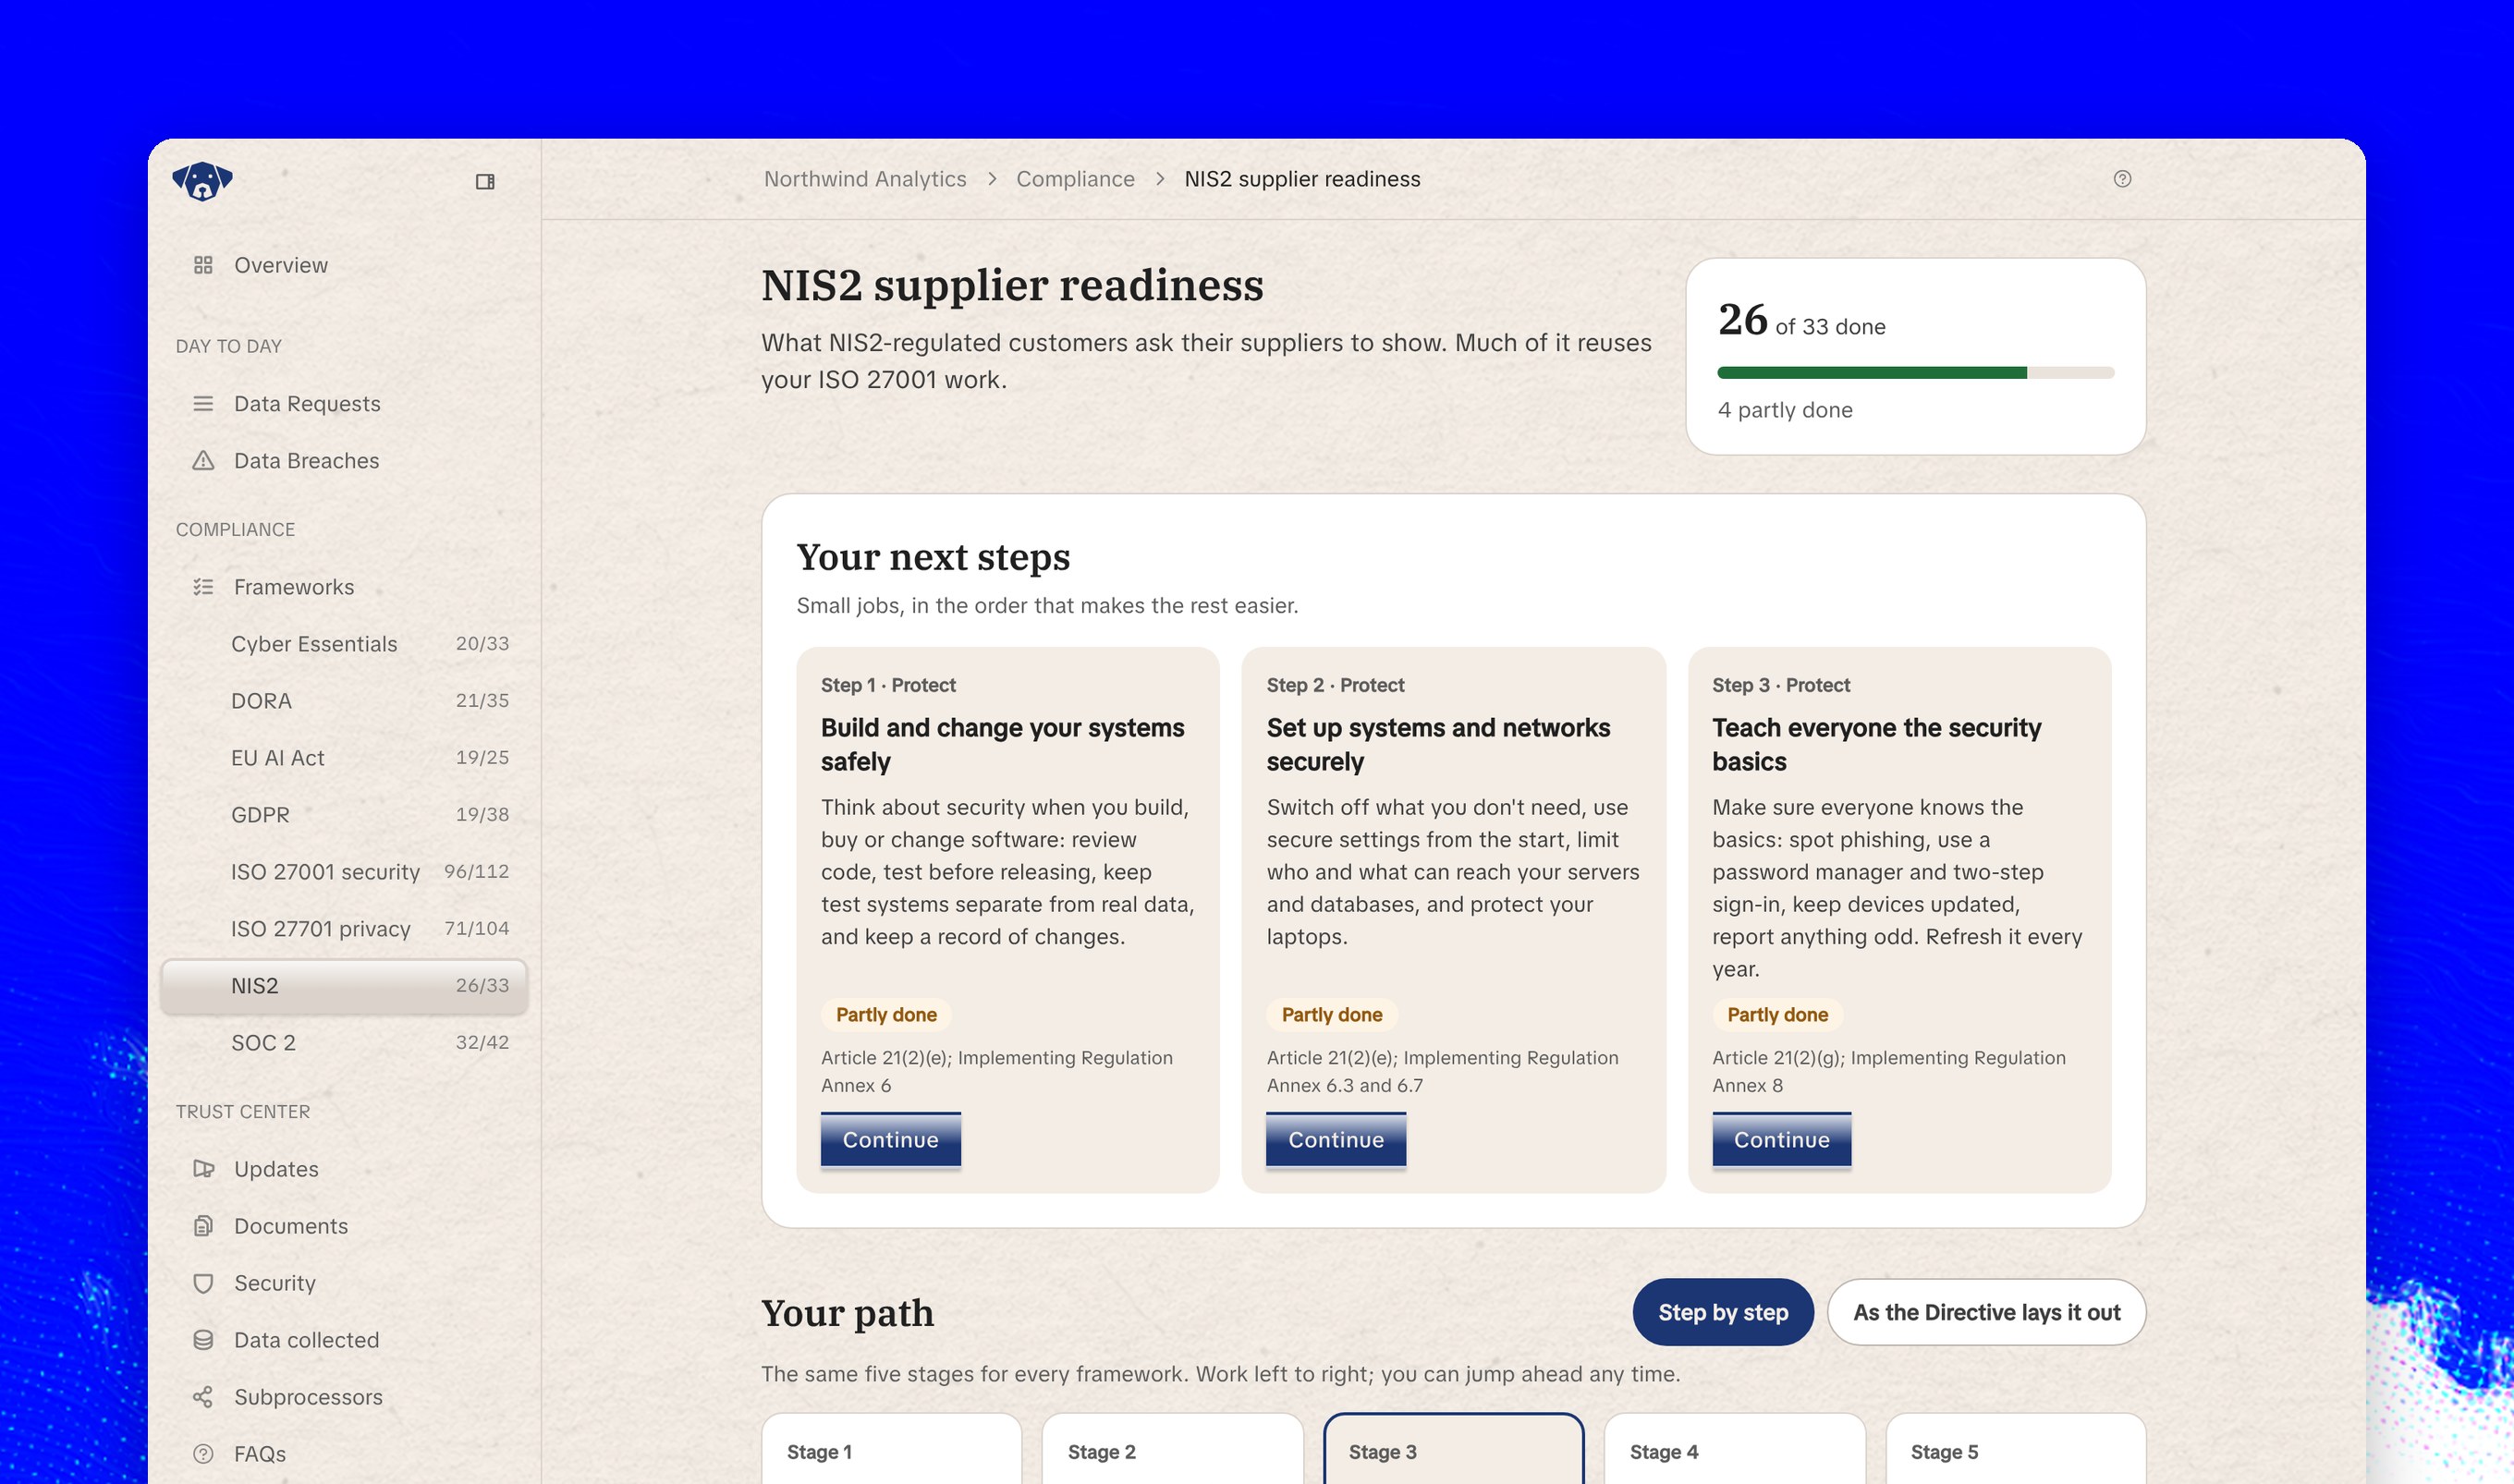
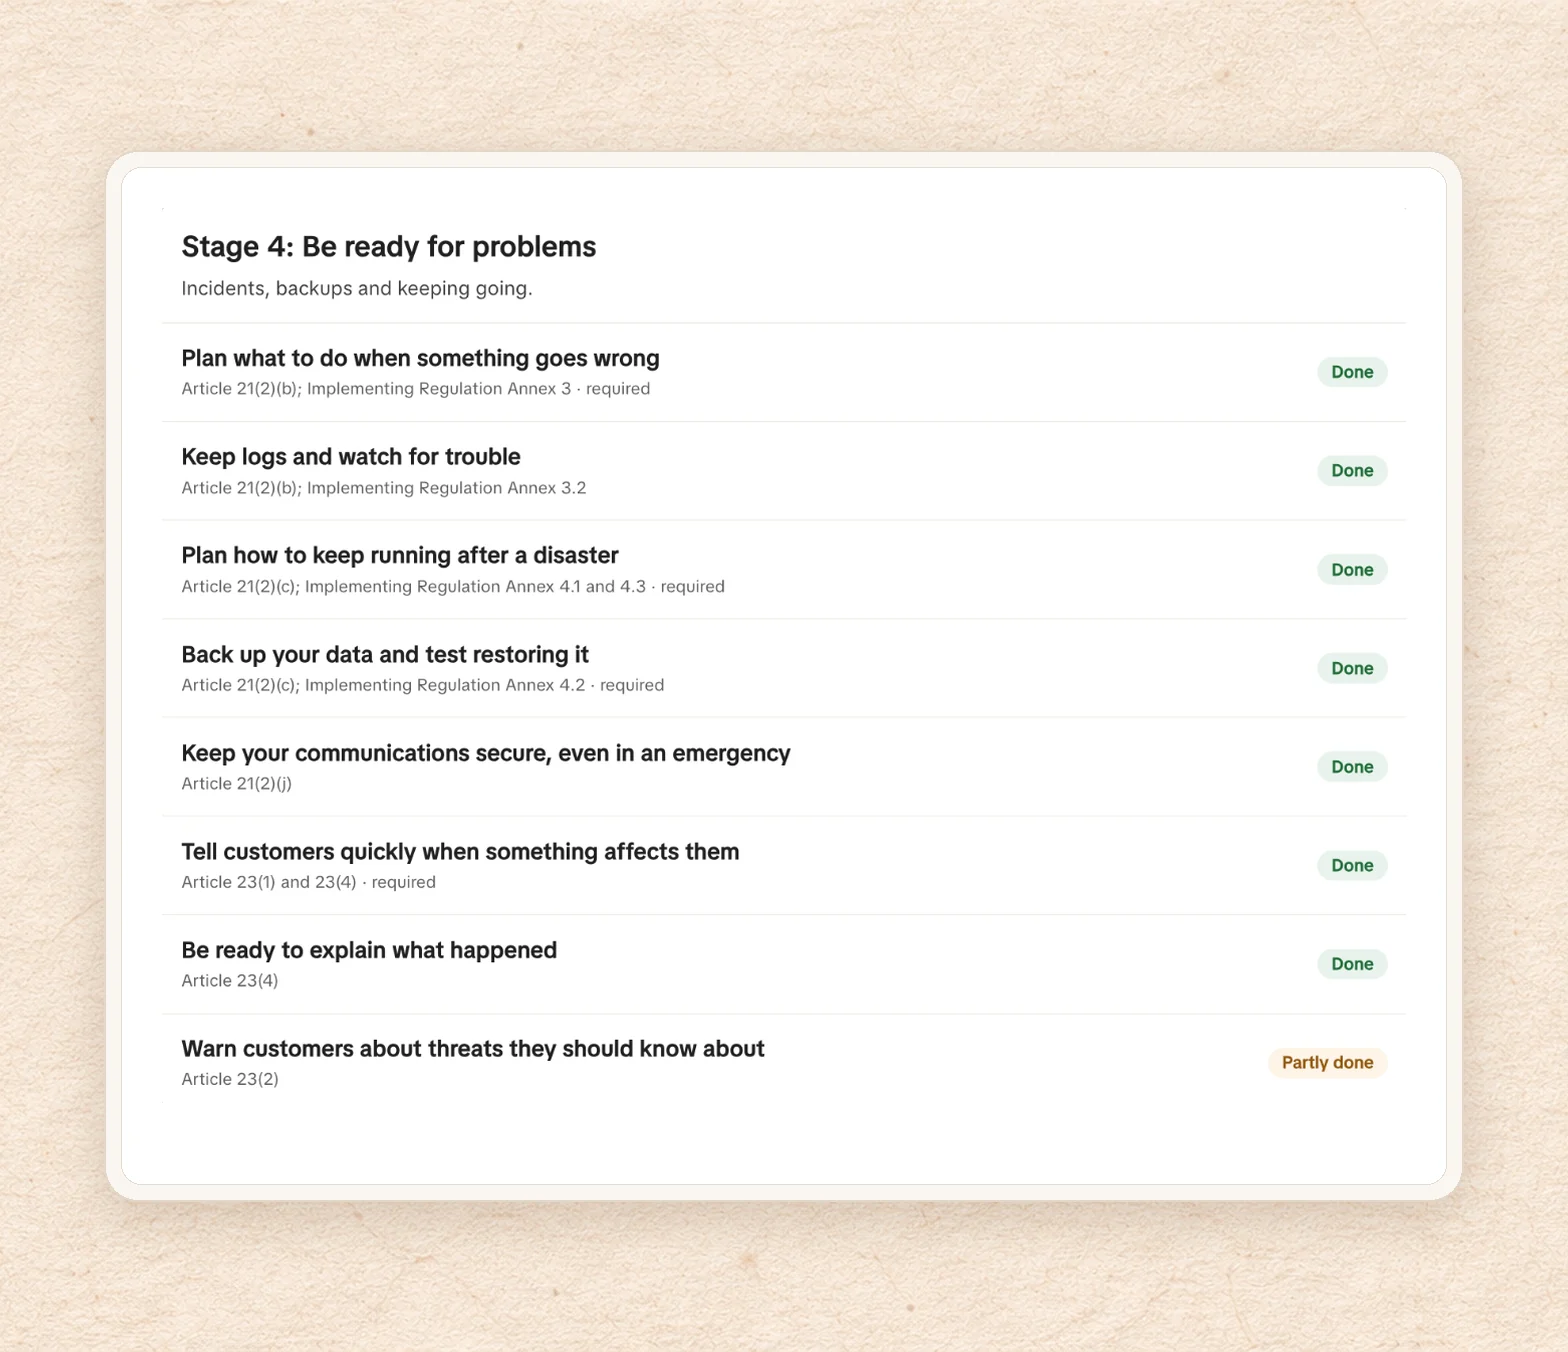
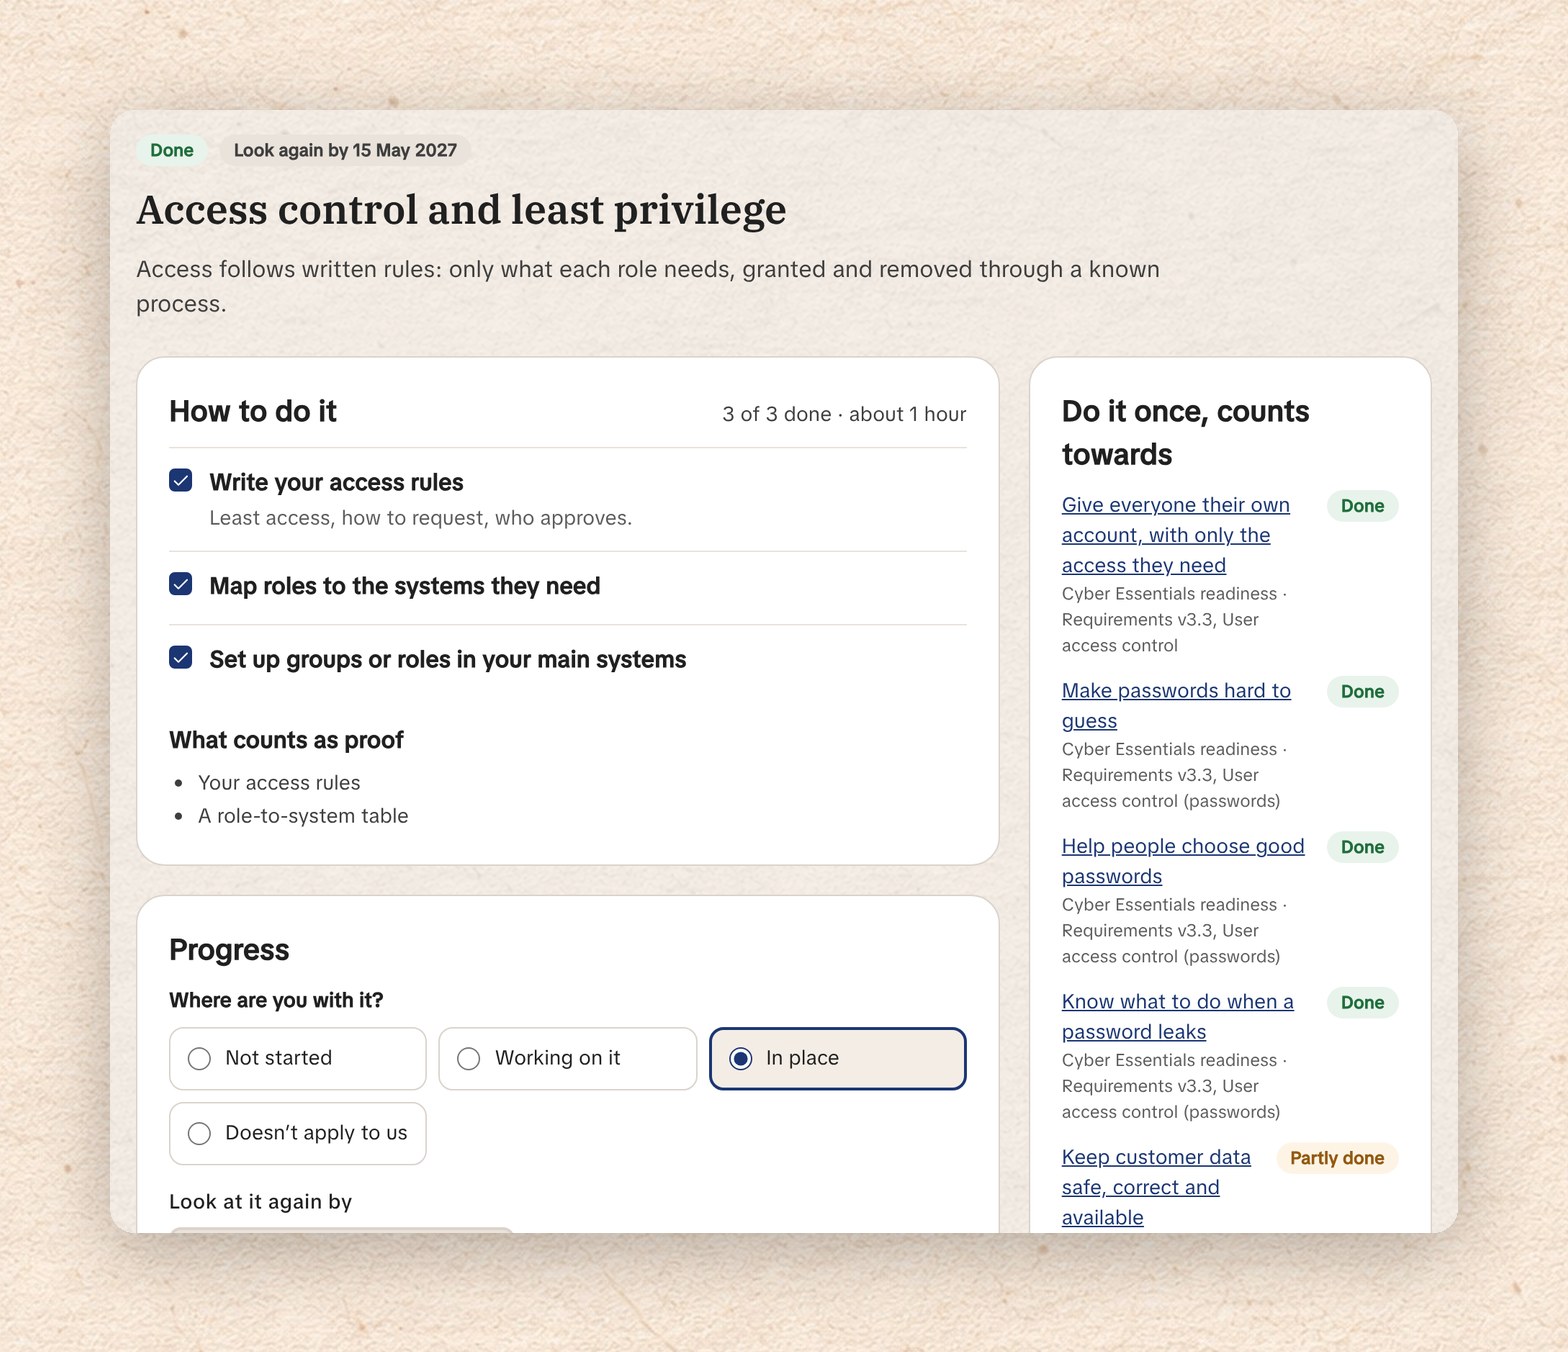
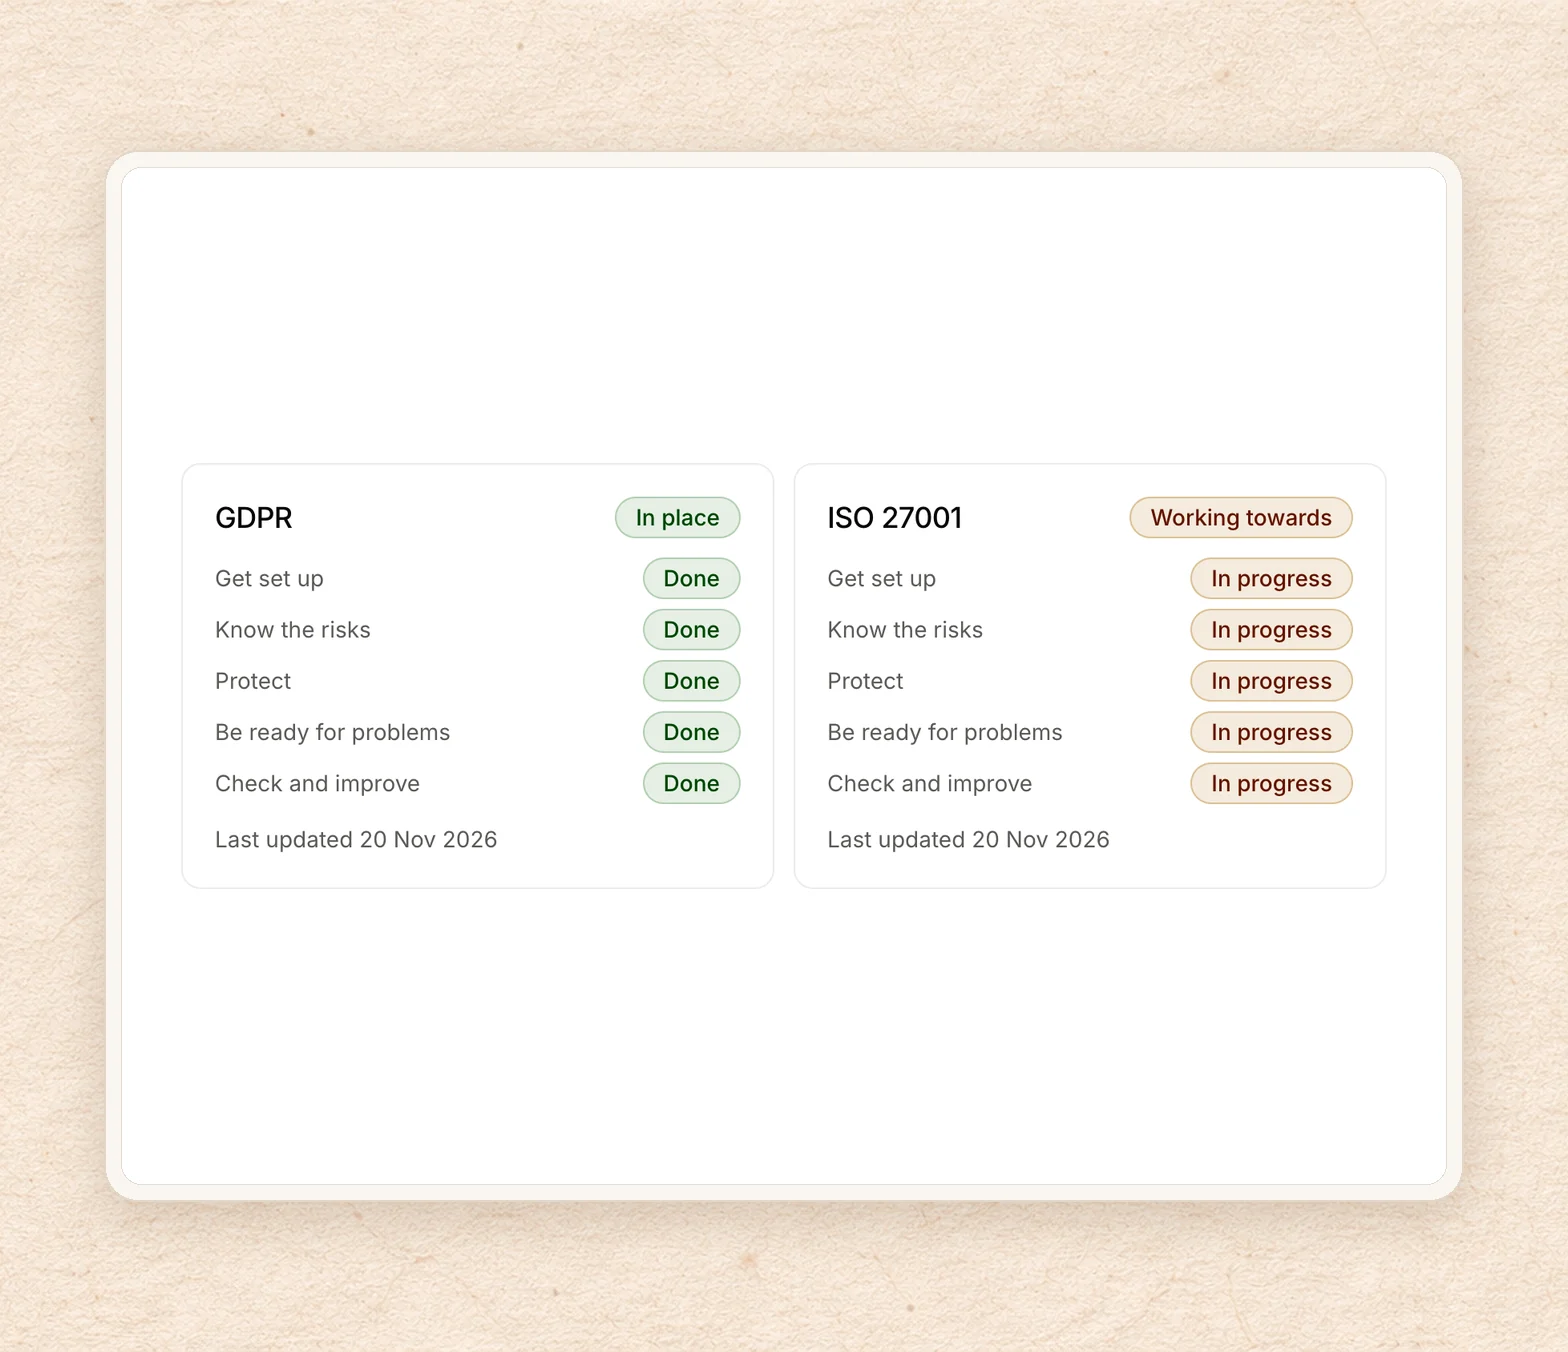
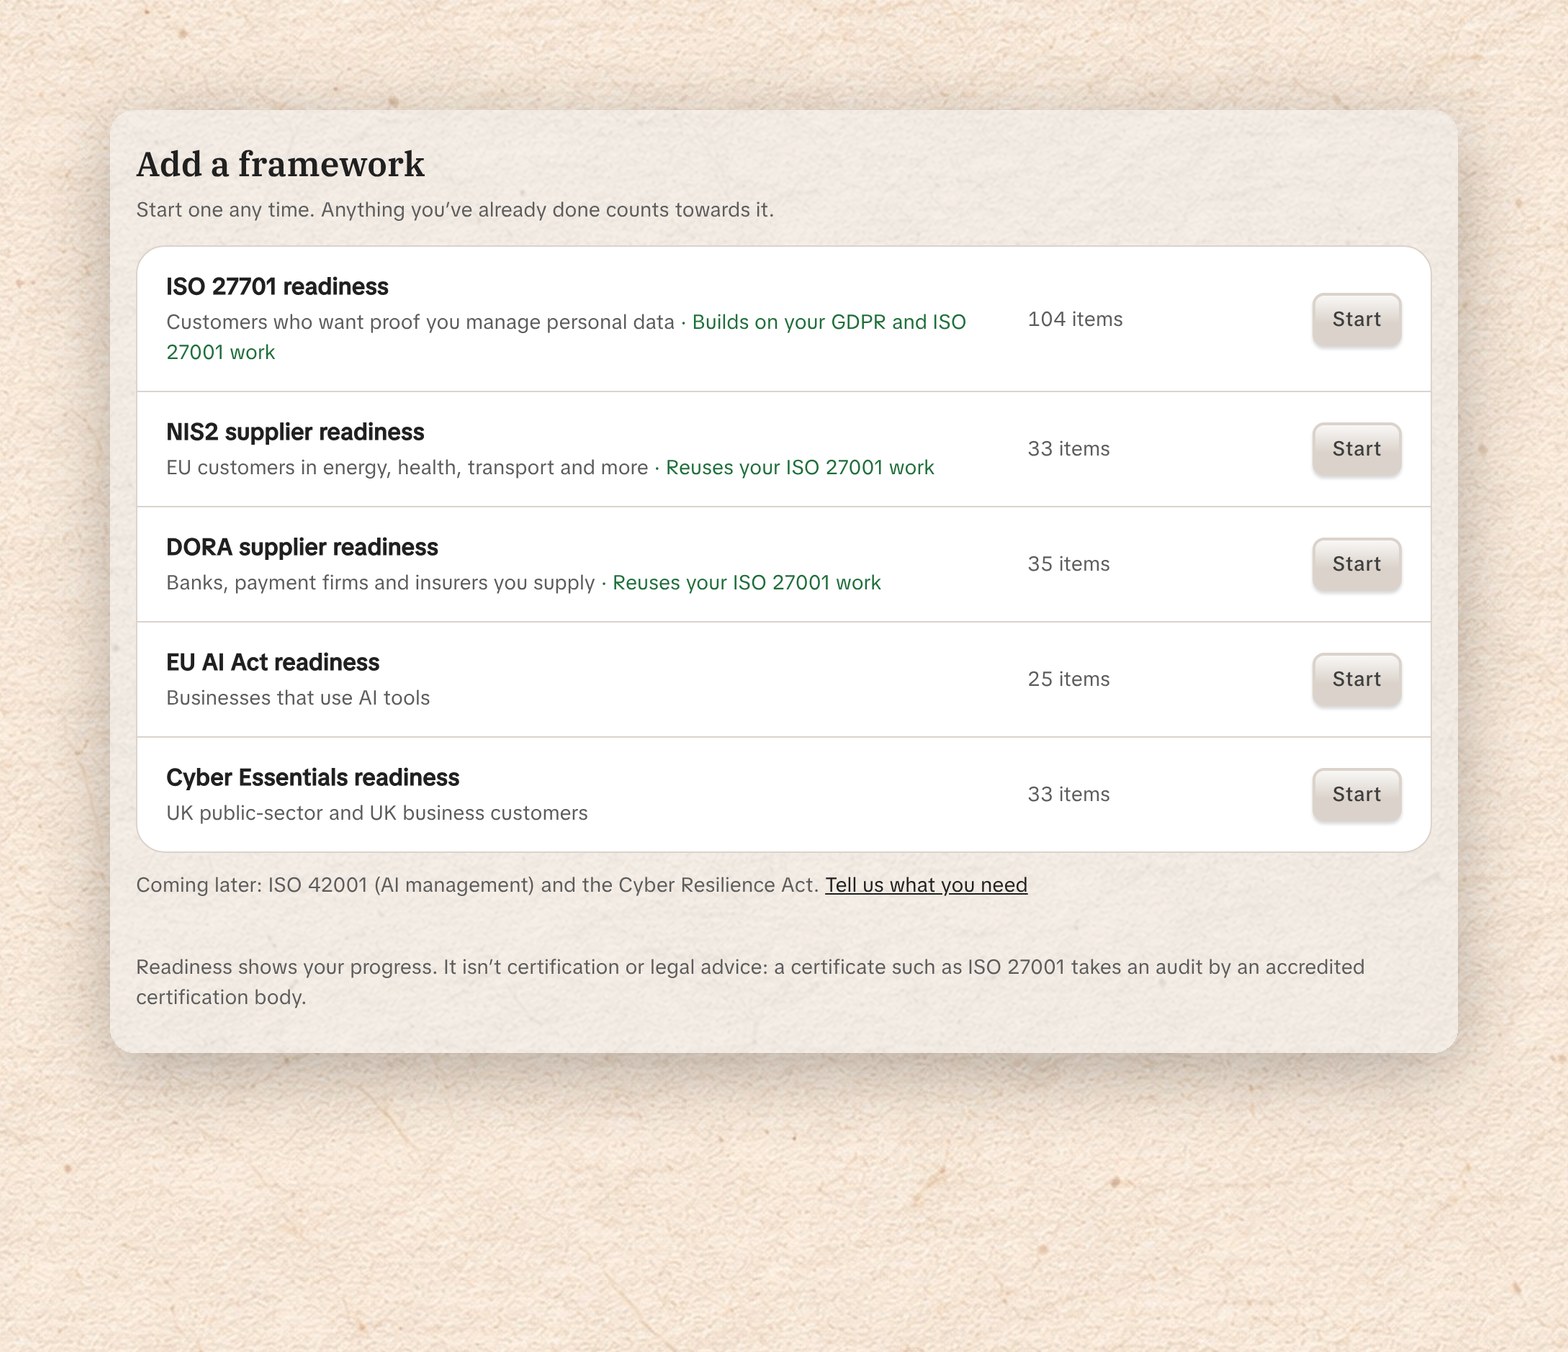
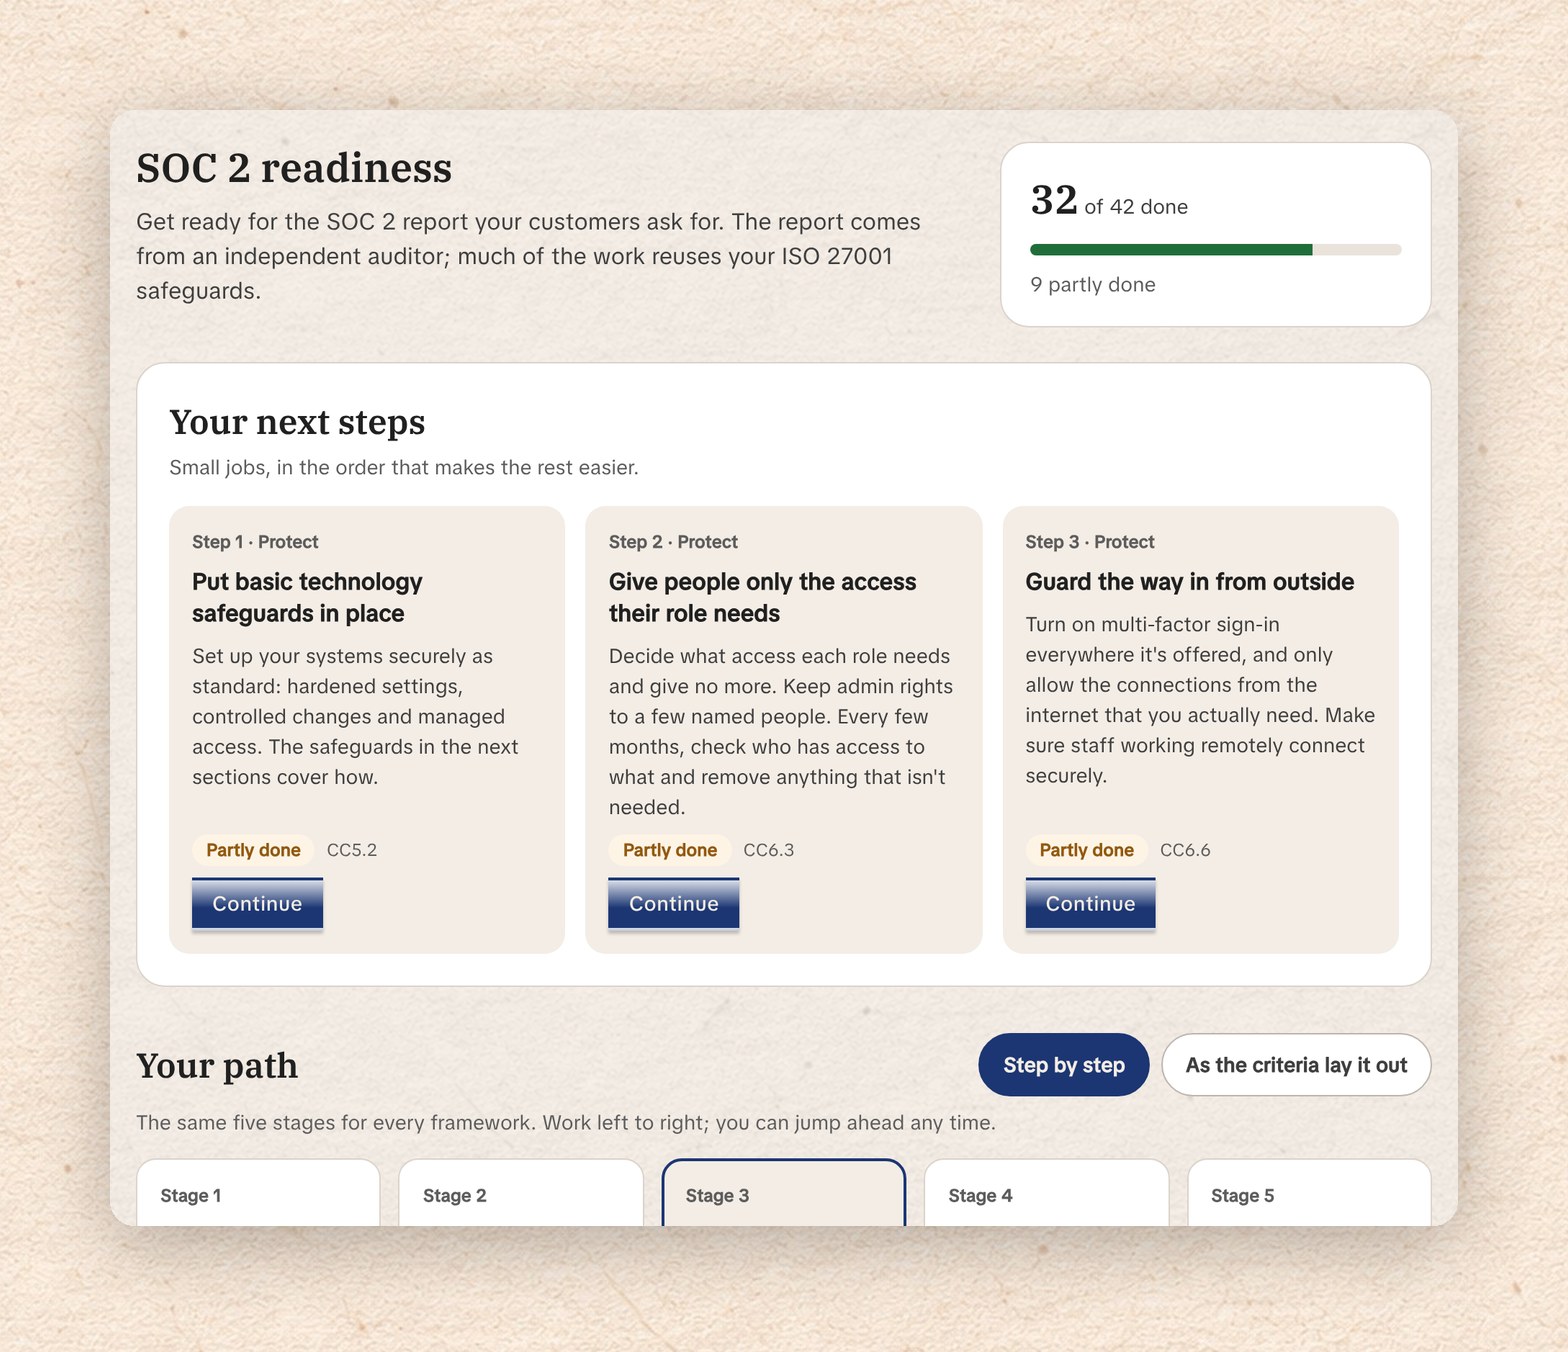
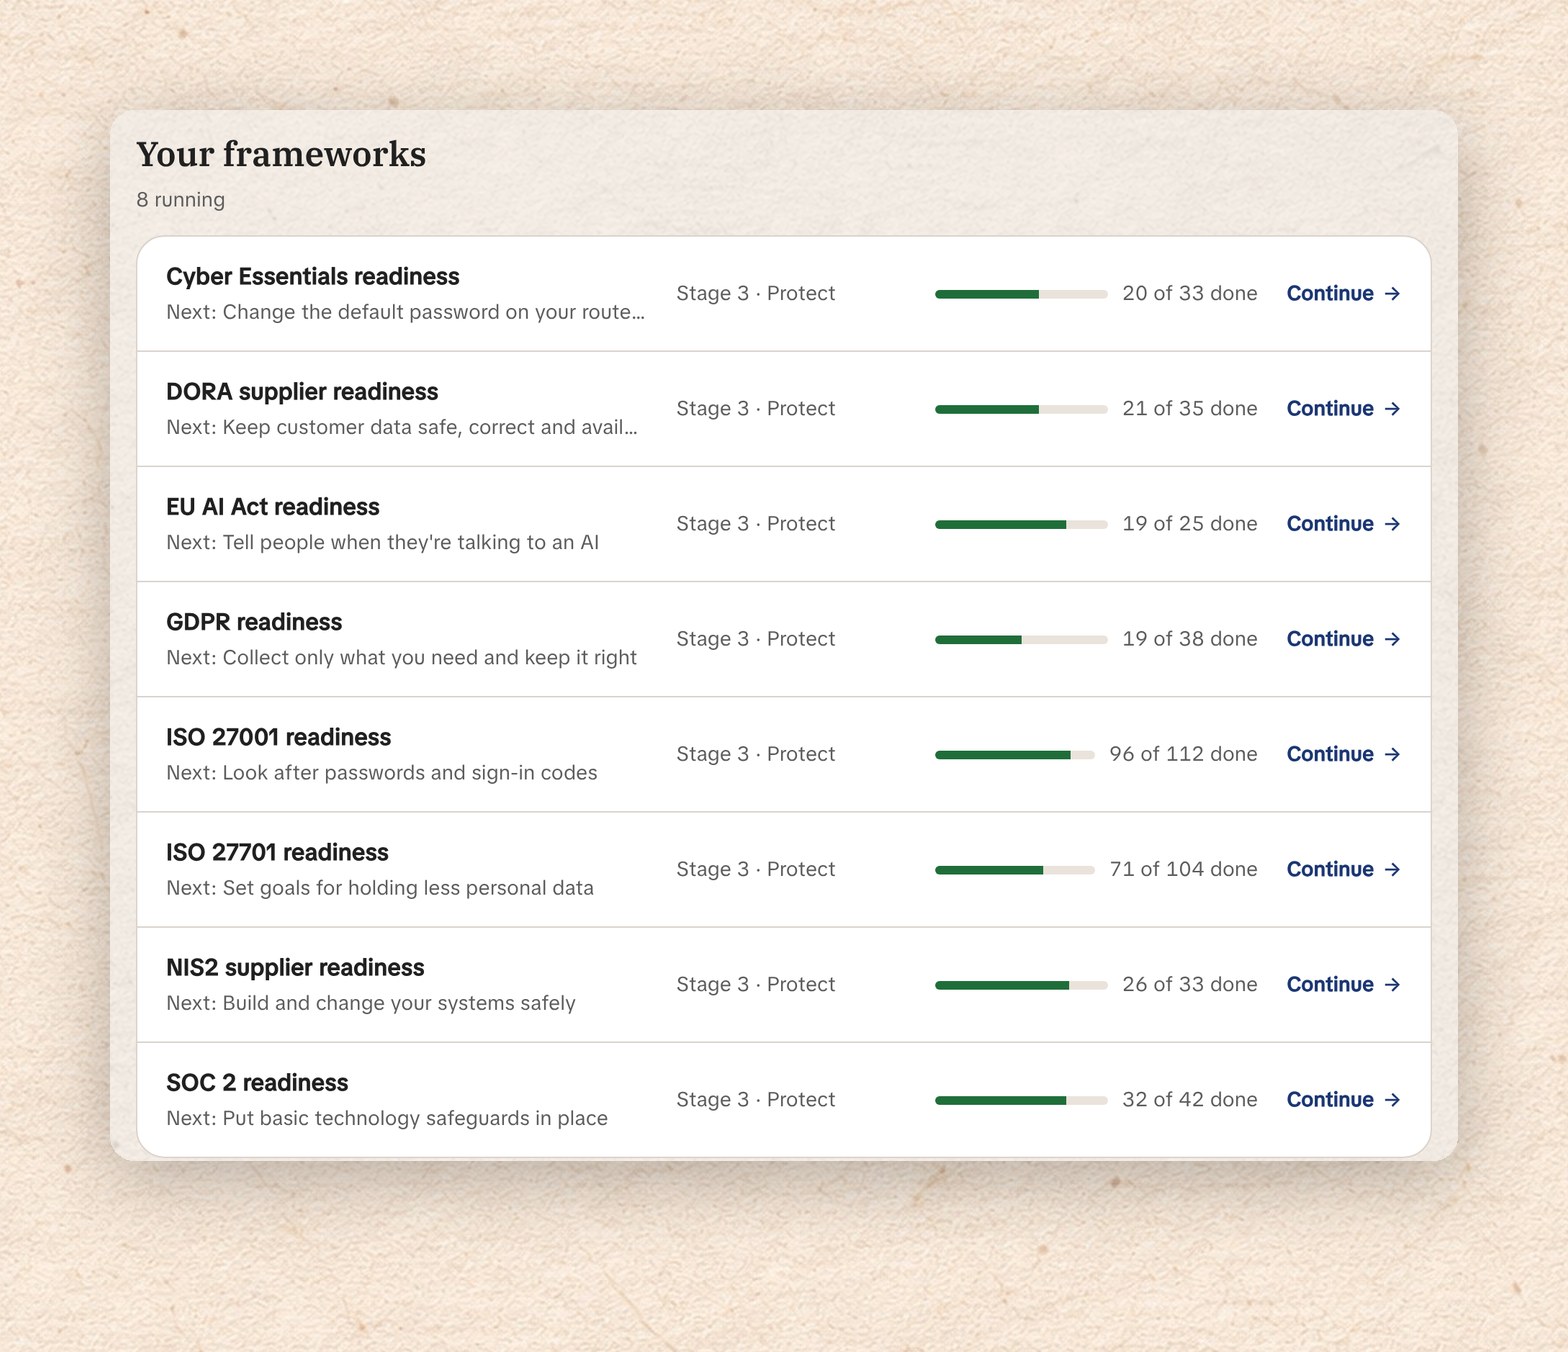
Next Steps and Readiness Score
The same layout as every ComplyDog framework, so nothing new to learn.
Incident Reporting
Know who to tell and when if something goes wrong, and keep a record in your breach log.
Your Suppliers, Listed
Your subprocessor list doubles as the supplier list customers ask about.
DPA Requests
Customers request your signed DPA from your portal.
Policy Templates
Start from plain-English policies, then make them yours.
Full History
See who changed what and when.
ComplyDog's NIS2 programme is built for suppliers to NIS2 companies. If NIS2 applies to you directly, you'll also have national registration and reporting duties. Check with your national authority.